Schneider Electric Strengthens Modicon PLC Cybersecurity for Industrial Automation and Water Operati
Time:2026-10-08 Browse: 0
Schneider Electric Advances PLC Cybersecurity for Industrial Automation
Schneider Electric has announced new cybersecurity enhancements for its Modicon automation portfolio as industrial operators face increasing pressure to protect operational technology systems.
The announcement was made in September 2026 during WEFTEC 2026 in New Orleans, where Schneider Electric presented technologies designed to modernize water and wastewater operations.
The company's latest Modicon release introduces enhanced cybersecurity capabilities across the automation architecture, including encrypted firmware, network authentication and role-based access control.
The new capabilities are designed around IEC 62443-3-3 Security Level 2 requirements and extend cybersecurity protections for Modicon M580 CPUs, communication cards, Ethernet switches and the Modicon Edge I/O NTS distributed I/O platform.
The development highlights a major issue facing modern industrial automation: cybersecurity is no longer separate from PLC and control system engineering.
Why PLC Cybersecurity Matters
Programmable logic controllers are at the center of many industrial systems.
They control motors, pumps, valves, conveyors, compressors, packaging machines and other critical equipment.
In water treatment plants, PLCs may control pumping stations, chemical dosing systems, filtration processes and other infrastructure.
In manufacturing facilities, PLCs can control entire production lines.
Historically, industrial control systems were often designed around reliability and physical isolation.
Modern industrial environments are much more connected.
Industrial Ethernet networks, remote monitoring, engineering workstations, cloud applications, IIoT devices and enterprise systems can create new communication paths between operational technology and information technology environments.
Connectivity provides major operational benefits, but it also creates new cybersecurity requirements.
A compromised industrial system can potentially affect production availability, equipment performance and even physical processes.
For this reason, cybersecurity must increasingly be considered during the design and maintenance of PLC systems.
Modicon PLCs and Secure Automation Architecture
Schneider Electric's latest Modicon enhancements reflect a broader movement toward secure-by-design automation.
Rather than treating cybersecurity as an additional product installed around the control system, security functions can be integrated into the automation architecture itself.
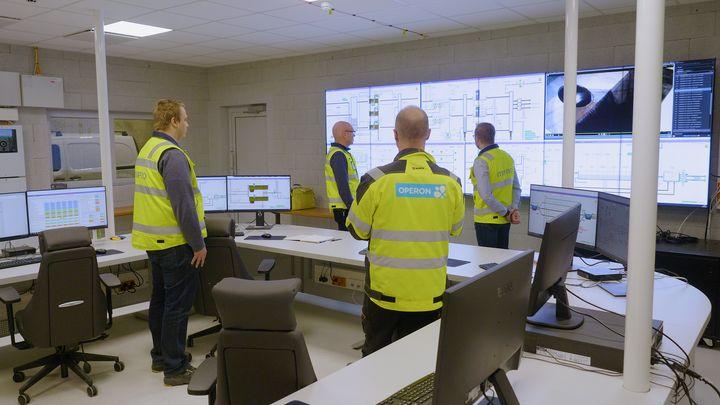
The Modicon ecosystem includes PLC CPUs, communication modules, industrial Ethernet infrastructure and distributed I/O.
Each component can represent an important part of the overall attack surface.
Protecting only the central PLC controller is therefore not enough.
A secure industrial architecture needs to consider controllers, network devices, engineering stations, remote I/O and communication paths.
This is especially important in large plants where hundreds or thousands of industrial devices may communicate continuously.
Encrypted Firmware Helps Protect the Control Platform
One of the new cybersecurity capabilities highlighted by Schneider Electric is encrypted firmware.
Firmware is a critical component of industrial automation hardware because it controls how the device operates.
Protecting firmware can help reduce the risk associated with unauthorized modification or manipulation of device software.
For industrial operators, this is important because automation hardware often remains in service for many years.
A PLC may operate continuously for a decade or longer, depending on the application and maintenance strategy.
During that time, the cybersecurity environment can change significantly.
Secure firmware mechanisms can therefore become an important component of long-term industrial cybersecurity.
Network Authentication Becomes Increasingly Important
Another major enhancement is network authentication.
Modern PLC systems increasingly communicate over Ethernet-based industrial networks.
This provides high-speed communication between controllers, I/O modules, drives, HMIs, SCADA systems and other devices.
However, simply connecting devices to a network does not automatically make the network secure.
Industrial networks need mechanisms that help ensure authorized devices and systems can communicate.
Authentication can therefore become an important layer in a defense-in-depth strategy.
For system integrators, this also means cybersecurity requirements need to be considered during network architecture design.
Network segmentation, authentication, access policies and monitoring can all contribute to a more resilient OT environment.
Role-Based Access Control for Industrial Systems
Role-based access control is another key capability highlighted in the latest Modicon release.
Industrial automation systems are typically operated by multiple types of users.
An automation engineer may need access to PLC programming and configuration.
A maintenance technician may need diagnostic access.
An operator may only need access to the HMI and process monitoring functions.
An IT or cybersecurity team may need access to security logs and network information.
Giving every user the same level of access creates unnecessary risk.
Role-based access control allows organizations to assign permissions according to job responsibilities.
This follows an important cybersecurity principle: users should receive the minimum access necessary to perform their work.
For industrial plants with multiple teams and contractors, this can become particularly important.
IEC 62443 and Industrial Cybersecurity
The growing adoption of IEC 62443 standards reflects the increasing maturity of industrial cybersecurity.
IEC 62443 provides a framework for addressing cybersecurity across industrial automation and control systems.
The standard recognizes that securing an industrial environment requires more than protecting individual devices.
It involves people, processes, systems, networks and technology.
Schneider Electric says its latest Modicon release is certified to IEC 62443-3-3 Security Level 2.
For automation professionals, this is important because industrial cybersecurity is increasingly becoming part of engineering specifications and procurement requirements.
System integrators may need to consider cybersecurity during the earliest stages of an automation project rather than treating it as a final commissioning task.
Water Infrastructure Creates Special Automation Challenges
The connection between Schneider Electric's Modicon cybersecurity developments and WEFTEC 2026 is particularly relevant.
Water and wastewater infrastructure is highly dependent on industrial automation.
Pumps, valves, sensors, chemical dosing systems and treatment processes need to operate reliably.
Many facilities also rely on SCADA and remote monitoring systems to manage geographically distributed infrastructure.
This creates a challenging cybersecurity environment.
A water utility may need to maintain equipment that has been installed for many years while simultaneously introducing modern networking and digital technologies.
Completely replacing existing infrastructure may not be economically or operationally realistic.
Modernization therefore needs to balance reliability, cybersecurity and investment protection.
Open and Software-Defined Automation
Schneider Electric is also emphasizing open, software-defined automation through its EcoStruxure Automation Expert platform.
This reflects another major trend in industrial automation.
Traditional automation architectures were often closely tied to specific hardware platforms.
Software-defined automation seeks to create greater flexibility by separating certain software functions from fixed hardware dependencies.
For manufacturers and utilities, this can make modernization more gradual.
Existing hardware can potentially remain part of the control architecture while new software capabilities are introduced.
This is particularly useful for plants where production cannot simply be stopped for a complete control system replacement.
Implications for Automation Engineers
The growing importance of industrial cybersecurity means that automation engineers need to think beyond PLC programming.
A modern PLC engineer may need to understand network architecture, user permissions, secure remote access, industrial Ethernet and cybersecurity requirements.
This does not mean every automation engineer needs to become a cybersecurity specialist.
However, cybersecurity awareness is increasingly becoming part of the normal automation engineering skill set.
During a PLC project, engineers may need to consider questions such as:
Who can access the controller?
How are engineering workstations authenticated?
Which devices can communicate with the PLC?
How are firmware updates protected?
How is remote access controlled?
What happens if an industrial network is compromised?
These questions are becoming just as relevant as traditional PLC programming and I/O configuration.